How do you stop Claude Code from touching sensitive files like .env? Deny Rules vs Hooks (interview question)
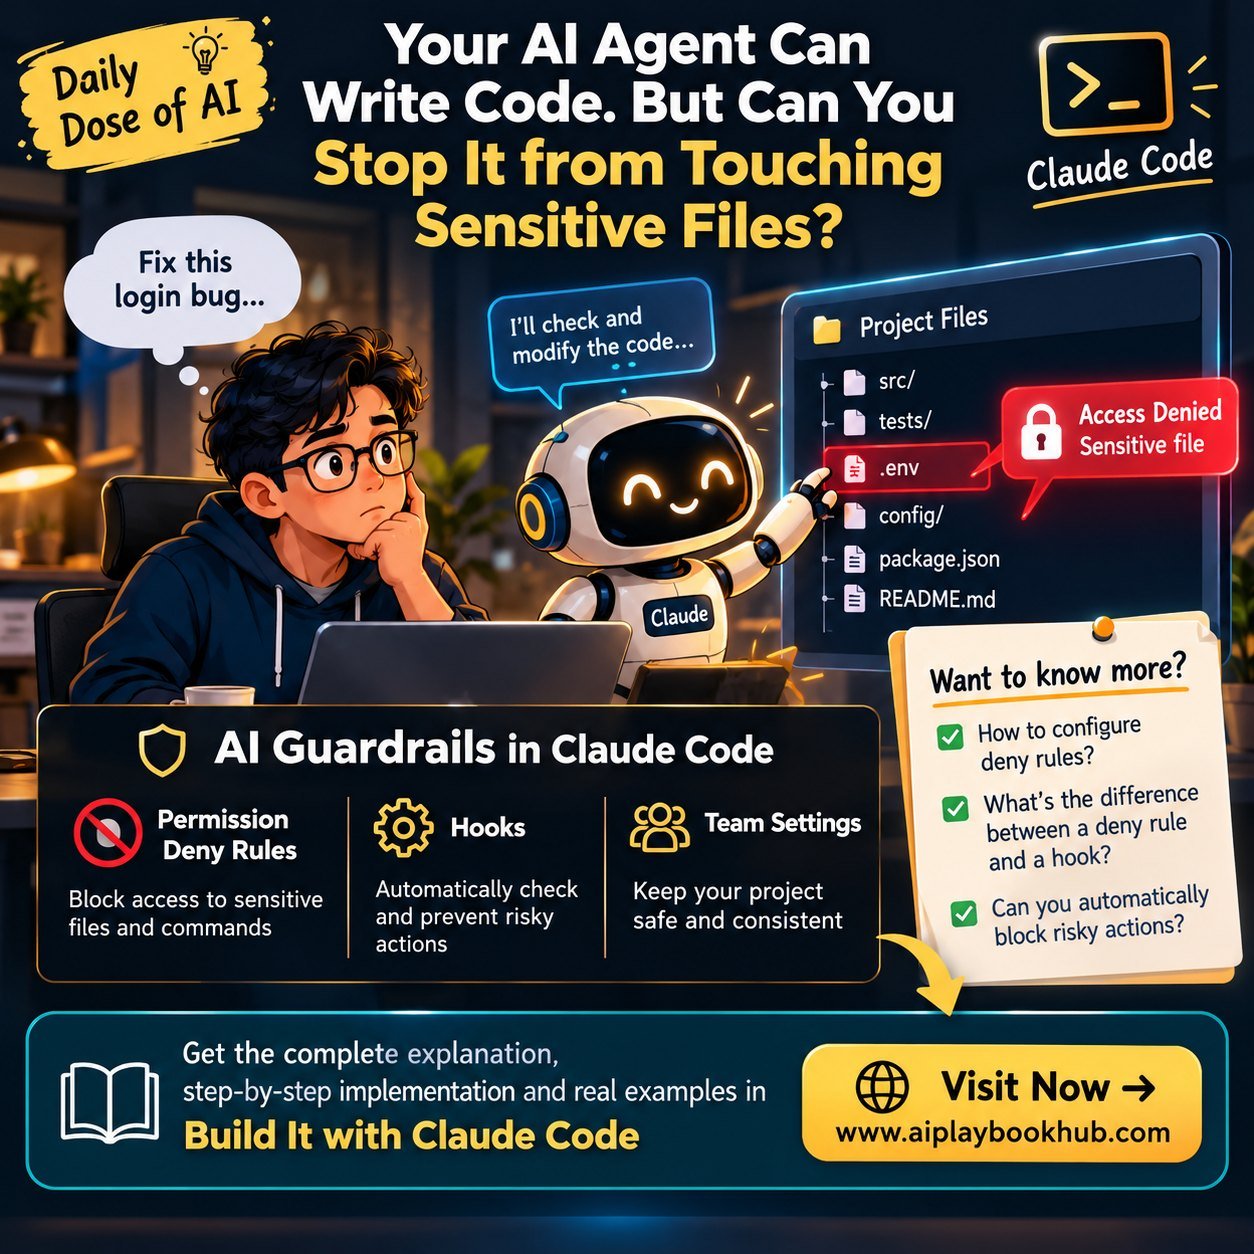
Claude Code gives you two ways to control what an AI agent can access and run. Permission Deny Rules block specific tools or file paths outright. Hooks run your own scripts before or after an action, so you can inspect it and block anything risky automatically
Your AI Agent Can Write Code. But Can You Stop It from Touching Sensitive Files?
Imagine asking Claude Code to fix a login bug.
What if it attempts to modify your .env file containing sensitive configuration?
Here's something important:
Claude Code supports Permission Deny Rules and Hooks to help control what an AI agent can access and execute.
But here's the interesting part... 👇
❓ How do you configure these rules?
❓ What's the difference between a Deny Rule and a Hook?
❓ Can you automatically block risky actions?
Covered the practical implementation and examples in my Claude Code guide.
👉 Explore the complete concept here with POC:
https://lnkd.in/dv_idBSH
🎯 Remember: Giving AI instructions is easy. Controlling its actions is what matters!